Offensive Security Leadership
Pentest practice leadership, methodology, QA, technical escalation, capability development, staffing, and delivery standards.
I’m Mike Shelton, Head of Pentesting at Red Sentry. My background spans offensive security leadership, technical project management, cybersecurity consulting, and IT operations.
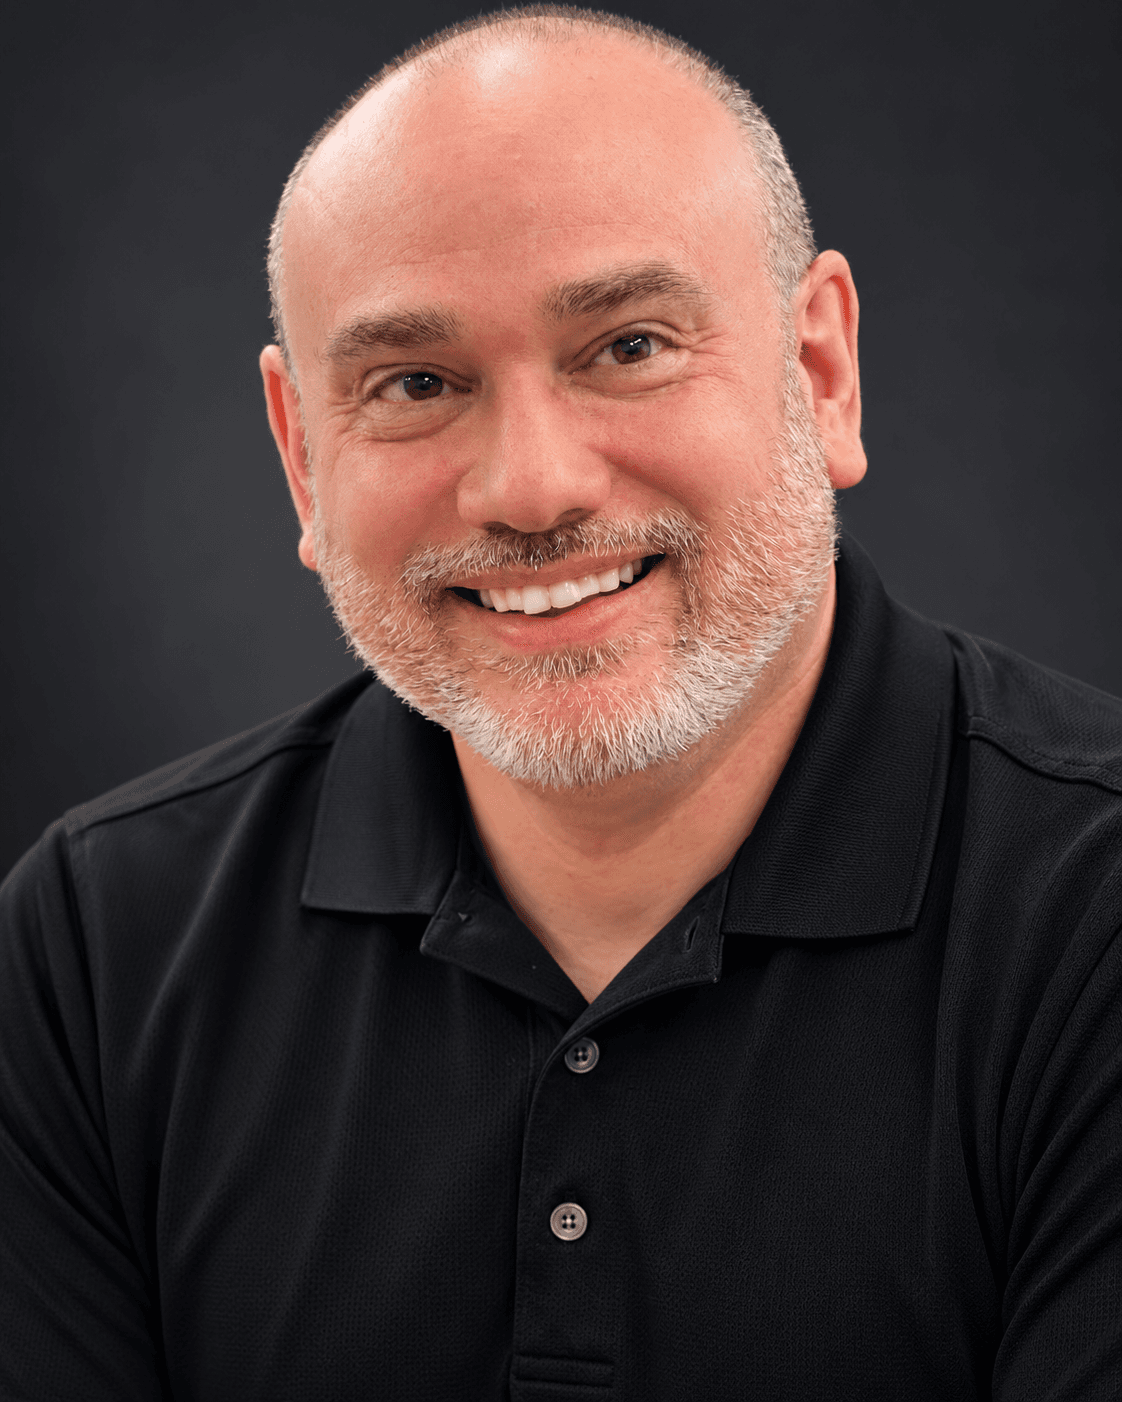
I lead the pentesting practice at Red Sentry, where my work spans technical leadership, project management, security delivery, team development, QA, resource planning, scoping, and client escalations.
My career has moved through IT support, systems administration, IT management, cybersecurity operations, security consulting, technical project management, and offensive security leadership. The common thread has been solving operational problems in technical environments.
I’m strongest when the work is complicated, ownership is unclear, and technical teams need a practical path from requirements to execution.
Pentest practice leadership, methodology, QA, technical escalation, capability development, staffing, and delivery standards.
Complex project delivery, scoping support, SOW alignment, scheduling, stakeholder communication, risk management, and closeout.
Security consulting operations across pentesting, reporting, remediation validation, client readouts, and delivery process improvement.
Infrastructure, systems administration, security controls, vulnerability management, migrations, support, and IT leadership.
Lead the penetration testing practice across delivery quality, methodology, QA, technical standards, team development, scoping support, resource planning, and client escalations.
Managed cybersecurity consulting delivery across client communication, technical teams, timelines, reporting, and engagement closeout.
Led delivery of cybersecurity consulting engagements and coordinated distributed technical teams across the full client lifecycle.
Managed security operations and controls across enterprise infrastructure in a banking environment.
Led IT operations, infrastructure, security, projects, and staff in a public-sector environment.
These examples are anonymized and focused on the operating problems, decisions, and outcomes rather than client-specific details.
Challenge
Engagement ownership, readiness, scheduling, and delivery expectations were inconsistent across Sales, PM, and testing.
Work
Defined clearer handoffs, delivery stages, access-readiness expectations, scheduling controls, QA ownership, and remediation workflows.
Impact
Created a more repeatable delivery model with clearer accountability and fewer mid-engagement surprises.
Challenge
Project count alone did not reflect actual tester workload, QA rotations, skill requirements, or contractor dependency.
Work
Built practical capacity planning around tester capability, QA rotations, project weight, contractor usage, and delivery windows.
Impact
Improved staffing visibility and made it easier to identify when internal capacity was exhausted before delivery quality suffered.
Challenge
Reporting consistency and technical capability varied across testers and assessment types.
Work
Strengthened QA expectations, severity consistency, technical review, skills tracking, mentorship, and training tied to real delivery needs.
Impact
Created clearer quality expectations while using recurring delivery issues to drive targeted team development.
Challenge
Technical scope, effort, staffing, and client timelines were not always aligned before delivery commitments were made.
Work
Connected scoping inputs to effort models, delivery assumptions, resource feasibility, and clearer SOW expectations.
Impact
Improved the handoff between Sales, scoping, PM, and testing while reducing avoidable scope and scheduling friction.
I write about offensive security, technical delivery, identity, attack paths, AI security, and the operating decisions behind reliable security work.
What changes when the target includes prompts, models, retrieval, tools, agents, and the application wrapped around them.
Read article Offensive SecurityWhy adversary simulation is different from simply making a penetration test larger or broader.
Read article Security DeliveryWhy workload planning breaks when every technical engagement is treated as equal.
Read articleAs Michael Shelton, I write The Echo Phantom Chronicles, fiction that explores technology, digital identity, justice, and the human consequences behind the screen.
The author site is intentionally separate from this professional portfolio, but the same cybersecurity background informs both.
Visit my author site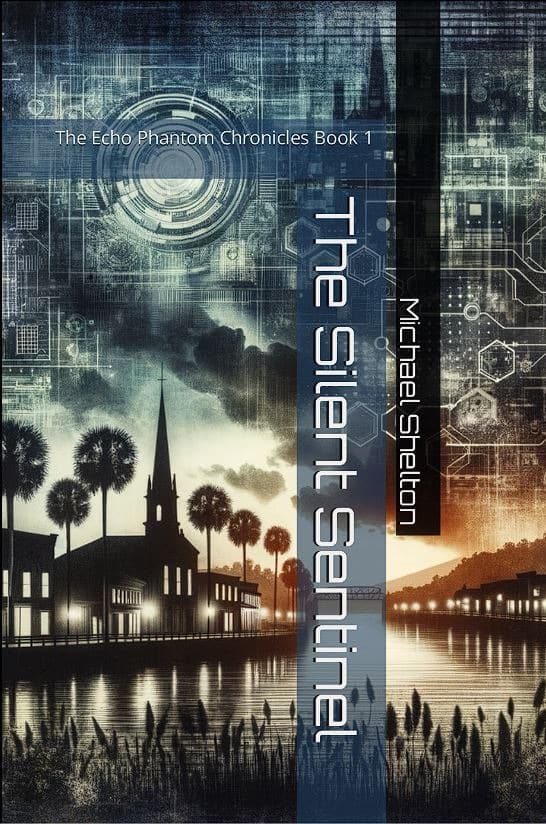 The Silent Sentinel
My job as a leader is to make the environment around technical people clearer, more sustainable, and easier to execute in.
Teams make better decisions when they understand the outcome, constraints, and why the work matters, not just the task in front of them.
I try to reduce avoidable churn, make workload visible, and keep urgent work from becoming the default way the team operates.
I prefer practical development tied to current delivery needs, technical review, mentorship, targeted training, and increasing ownership over time.
I value calm, specific feedback and clear expectations. The goal is to fix the issue without creating unnecessary drama around it.
These are practical operating principles I use across security delivery, project management, team leadership, and cross-functional work.
Ambiguity creates rework and burnout. I prefer clear owners, decision points, handoffs, and escalation paths before work becomes urgent.
Good outcomes should not depend on heroics. Methodology, QA, reporting, and delivery controls should make quality repeatable.
Workload has to account for complexity, skill fit, QA duties, dependencies, client readiness, and the actual effort required to deliver well.
Short-term coverage is sometimes necessary, but temporary workarounds should not quietly become the operating model.
When something is at risk, I try to surface it early with the tradeoffs, consequences, and a practical decision to make.
Sales, PM, delivery, Product, and leadership need a shared understanding of scope, risk, assumptions, and what success actually requires.
Selected recommendations from people who have managed or worked alongside me across cybersecurity delivery and IT operations.
“As a Technical Project Manager, Mike led numerous security assessments for one of IncludeSec’s largest clients. He effectively addressed their particular needs and swiftly adapted to regular client-driven changes in process. He’s passionate about cyber security and I’d recommend him to anyone looking for a project manager in the cyber security space.”
“I really appreciated how he did such a great job managing the project, communicating with stake holders, and kept on top of issues till they were resolved. Not only is he technically great but he is also a great person.”
“Michael’s strong technical knowledge, coupled with a proactive attitude and dedication to excellence, raised our operational capacity to an entirely new level and gave us that extra sharp edge.”
Before moving fully into cybersecurity consulting, I spent years in infrastructure, systems administration, IT management, banking technology, healthcare IT, and public-sector environments.
My background fits roles where technical security, project delivery, and operational leadership overlap. I’m especially interested in offensive security leadership, technical project management, cybersecurity delivery, security consulting operations, and IT leadership.
Send me a note here. The form delivers the message privately without publishing my email address in the page source.